The Standard in Secure Tax AI
Black Ore protects sensitive client data through independently audited security controls and U.S.-based processing. Your information is never used to train AI models.
Data Security & Infrastructure
Your security team will want specifics. Black Ore keeps client data encrypted, isolated between firms, and stored in U.S.-based data centers under continuous security monitoring.
Client Data Protection
Retain ownership and control of client data, including who can access it and when it can be exported or deleted. Client documents are never used to train AI models.

No Outsourced Access
Your client data is never handled by third-party teams. All processing stays within Black Ore’s secure, closed-loop platform.


Encrypted Processing
All processing occurs in encrypted, access-controlled environments.

Secure by Design
Security controls protect client data throughout the workflow, from document intake through preparation and review.

Full Data Ownership
Your firm retains full control and ownership of its data. Black Ore never uses client documents for model training or cross-firm optimization

Data Lifecycle Control
Export, redact, or delete data anytime—ensuring full lifecycle control and compliance

Independent Validation
SOC 2–compliant and independently audited, Black Ore’s infrastructure and controls meet the highest standards for enterprise-grade security
Access Controls & Permissions
Control who can access client information, make changes, and approve work across your teams and offices.
Role-Based Permissions
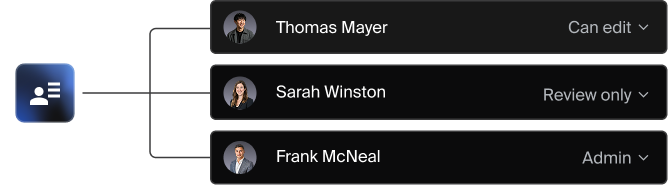
Set permissions for preparers, reviewers, managers and partners so each professional has access to the information and functions their role requires.
Multi-Level Security
Apply access rules at the return, document or field level to reflect how your firm assigns and reviews work.

Enterprise Authentication
Single Sign-On (SSO), Multi-Factor Authentication (MFA), and session management

Policy & Workflow Controls
Configure override permissions, approval stages and sign-off requirements according to your firm's review procedures.

Complete Audit Logging
Maintain full visibility. Every user action, data change, and workflow event is recorded and timestamped for compliance, oversight, and traceability
Compliance & Certifications
Black Ore's security controls are independently audited under SOC 2 Type II against the AICPA Trust Services Criteria for Security, Availability, and Confidentiality.


Security Is Foundational to Black Ore
Black Ore conducts quarterly security reviews and monitors its systems for threats throughout the year. Established incident-response procedures are in place to address issues when they arise.
FAQ — Security
Black Ore is SOC 2 Type II compliant and follows the AICPA Trust Services Criteria for Security, Availability, and Confidentiality. Our infrastructure includes enterprise-grade encryption (AES-256 at rest, TLS 1.2+ in transit), continuous monitoring, and strict access controls to keep your data protected at every layer.
No. Black Ore does not use sensitive client data to train models or share it with third-party services. Your data remains encrypted, protected and is never repurposed.
All client data is stored exclusively in U.S.-based, SOC 2-audited data centers. We do not offshore or outsource processing—your documents and extracted data never leave Black Ore’s secure environment.
Yes. Firms can set granular, role-based permissions across preparers, reviewers, managers, and partners—along with return-level, document-level, and field-level access policies.
Yes. Black Ore supports Single Sign-On (SSO), Multi-Factor Authentication (MFA), and customizable session management. Firms can enforce org-wide policies to meet internal IT and compliance requirements.
Bring us your toughest security questions.